
1. Introduction: Digital Identity, Privacy, and the Anonymity Illusion
In today’s hyper-connected digital landscape, the internet powers nearly every facet of our daily lives. From online banking and e-commerce to social media, remote work, and streaming, we spend hours online. Yet, very few users understand the complex background mechanisms that identify and track their devices across the web.
- 1. Introduction: Digital Identity, Privacy, and the Anonymity Illusion
- The Misconception: “I Turned On a VPN, So I’m 100% Invisible!”
- Backed by 16 Years of Hands-On Field Experience
- 2. Understanding IP Addresses: The Foundational Mechanics
- What is an IP Address and How Does Traffic Route?
- IPv4 vs. IPv6: The Structural Evolution
- Categories of IP Addresses
- What Sensitive Data Does Your IP Address Leak?
- 3. How VPNs Work & IP Masking Mechanics
- What is a VPN and How Does It Encrypt Traffic?
- The Process of IP Masking
- Key VPN Protocols Explained Simply
- The Limitations of Basic IP Masking
- 4. The Anonymity Gap: Device Fingerprinting Deep-Dive
- Why Changing Your IP Address Alone Fails
- How Device Fingerprinting Works Behind the Scenes
- The Uniqueness Math: How Trackers Identify You
- 5. Advanced Mitigation: How to Spoof and Neutralize Device Fingerprints
- Method 1: Anti-Detect Browsers (The Gold Standard)
- Method 2: Privacy-Hardened Browsers and Extensions
- Method 3: Hardware and Environment Synchronization
- Step-by-Step Blueprint for Complete Anonymity
- 6. Free vs. Paid VPNs: The Hidden Risks and Technical Realities
- The Hidden Trap of “Free” VPN Services
- Key Features of a Legitimate, Paid VPN Service
- Comparison Summary: Free vs. Paid VPNs
- 7. How to Choose a VPN & Debunking Common Anonymity Myths
- The Technical Evaluation Framework: How to Choose a VPN
- Debunking Common Anonymity Misconceptions
- Is Naye Format Se Issue Hamesha Ke Liye Khatam Kyun Hoga?
- Summary Table: Core Myths vs. Technical Realities
- 8. Conclusion & Final Recommendations
Traditionally, users rely on an IP Address (Internet Protocol Address) as their primary digital footprint. Just as a physical home address ensures mail reaches your doorstep, an IP address acts as a unique numerical identifier. It is assigned to every device connected to the internet, whether it is a smartphone, laptop, smart TV, or router.
The Misconception: “I Turned On a VPN, So I’m 100% Invisible!”
One of the most widespread myths among internet users is that simply toggling on a VPN (Virtual Private Network) or changing an IP address makes them completely anonymous online.
This is a dangerous misconception.
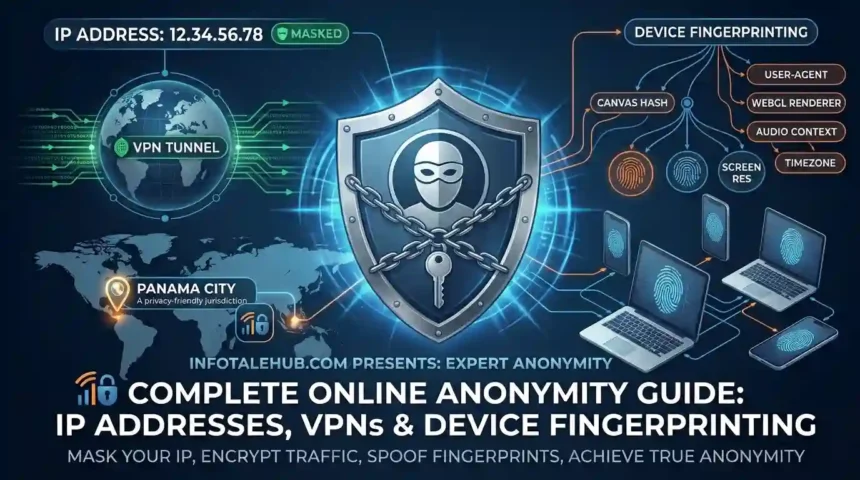
A VPN successfully masks your IP address and encrypts network traffic. However, changing your IP alone does not make you fully invisible. Modern tracking networks and sophisticated web servers no longer rely solely on IP addresses to identify users. Instead, they utilize Device Fingerprinting, as documented in [EFF digital privacy research]. This intrusive tracking method analyzes hardware and browser parameters, including:
- Browser Specifications: Engine version, installed extensions, and user-agent strings.
- Hardware Profiles: Screen resolution, GPU renderer (Canvas/WebGL fingerprinting), and audio context APIs.
- System Identifiers: Active system fonts, CPU core count, device orientation parameters, and exact time-zone configurations.
Tracking scripts stitch these unique telemetry data points together. They create a distinct “Digital Fingerprint” that identifies you with startling accuracy, even if your IP address changes every minute.
Backed by 16 Years of Hands-On Field Experience
Everything shared in this comprehensive guide is not theoretical knowledge copied from basic blogs. It is built on my 16 years of hands-on experience in digital privacy, network management, and cybersecurity testing. Over the past decade and a half, I have tested, analyzed, and bypassed nearly every tracking mechanism deployed on the web.
I am sharing these exact real-world techniques to teach you how to move beyond surface-level privacy tools. With these steps, you can achieve true, uncompromised online anonymity.
2. Understanding IP Addresses: The Foundational Mechanics
Before diving into advanced anonymization techniques, you must understand what an IP address actually is. It is essential to learn how it routes your internet traffic and what sensitive information it leaks about you.
What is an IP Address and How Does Traffic Route?
An Internet Protocol (IP) Address is a unique numerical label assigned to every device connected to a computer network. It serves two primary functions:
- Host Identification: Specifying who and what your device is on the network.
- Location Addressing: Providing the exact routing path so data packets reach your specific device.
Your traffic flows in a specific chain when you send a request online:
- Your Device connects to your Local Router.
- Your router routes the request through your Internet Service Provider (ISP).
- Your ISP assigns a Public IP Address to fetch the requested page from the Target Website.
IPv4 vs. IPv6: The Structural Evolution
Two active versions of IP addresses currently operate across the global internet infrastructure:
- IPv4 (Internet Protocol Version 4):
- Format: Written as a 32-bit numeric address separated by dots (Example:
192.168.1.1). - Capacity: Supports roughly 4.3 billion unique addresses.
- Current Status: IPv4 addresses are practically exhausted globally due to the explosion of modern internet devices. This shortage led to widespread use of network address translation (NAT).
- Format: Written as a 32-bit numeric address separated by dots (Example:
- IPv6 (Internet Protocol Version 6):
- Format: Written as a 128-bit alphanumeric address separated by colons (Example:
2001:0db8:85a3:0000:0000:8a2e:0370:7334). - Capacity: Supports $3.4 \times 10^{38}$ unique addresses, making it virtually unlimited.
- Privacy Impact: IPv6 addresses assign unique prefixes directly to end-user devices. This setup can make long-term tracking easier if privacy settings are not properly configured.
- Format: Written as a 128-bit alphanumeric address separated by colons (Example:
Categories of IP Addresses
- Public IP Address: The primary address visible to the outer internet, assigned directly by your ISP.
- Private IP Address: Internal network addresses used only inside your home or office Wi-Fi (Example:
192.168.1.1), hidden completely from the public web. - Dynamic IP Address: Automatically assigned by your ISP, this address changes periodically or every time your router restarts.
- Static IP Address: A permanent, fixed address commonly used for servers. It poses a severe tracking risk because your digital identity never changes.
What Sensitive Data Does Your IP Address Leak?
An IP address does not reveal your street name or personal identity directly. However, it leaks critical data to every server you touch:
- Geographic Location: Your exact country, city, region, and postal code zone.
- Internet Provider Info: The specific network provider (ISP) you are using.
- Potential Attack Vectors: Exposing your public IP address leaves your system vulnerable to port scanning, targeted DDoS attacks, and direct network intrusions.
3. How VPNs Work & IP Masking Mechanics
Now you understand how IP addresses function as your digital footprint. The next logical question is: How do we mask or change this IP address? This is where a Virtual Private Network (VPN) comes into play.
Most people use VPNs daily with a single tap on an app. However, very few understand the complex network layer mechanisms happening behind the scenes.
What is a VPN and How Does It Encrypt Traffic?
A Virtual Private Network (VPN) is a security technology. It creates a private, encrypted network connection over a public or unencrypted internet connection.
Without a VPN, your internet traffic is completely exposed. Your web browser connects directly to your Internet Service Provider (ISP). Then, your ISP routes your data to the target website’s server. During this unencrypted journey, your public IP address, location, and web requests are visible. ISPs, government entities, network administrators, and hackers on public Wi-Fi can see this data.
When you enable a VPN, two major security processes occur simultaneously:
- Traffic Encryption: Before leaving your device, all outgoing network traffic is scrambled using high-grade encryption algorithms (such as AES-256 or ChaCha20). Intercepted data packets will only appear as unreadable gibberish.
- Secure Tunneling: The encrypted data travels through a virtual “tunnel” directly to a remote server operated by your VPN provider.
The Process of IP Masking
The following transformation takes place once your encrypted data reaches the remote VPN server:
- Decryption and Forwarding: The VPN server decrypts your data packet. Afterwards, it forwards the request to the target website on your behalf.
- IP Substitution (Masking): To the destination website, the request appears to originate directly from the VPN server instead of your home router. The website sees the VPN server’s IP address and location, while your real public IP address remains hidden.
- The Return Journey: When the target website responds, it sends data back to the VPN server’s IP address. The VPN server encrypts this incoming response and routes it back through the secure tunnel to your device. Finally, your VPN software decrypts it for you to view.
Key VPN Protocols Explained Simply
The performance, speed, and security of a VPN depend heavily on its Tunneling Protocol. A protocol is essentially a set of mathematical rules determining how data is encrypted and transmitted through the tunnel.
- WireGuard:
- Best For: High speed, low latency, and modern security.
- Overview: WireGuard is the newest and most efficient VPN protocol. It uses lightweight code (around 4,000 lines compared to OpenVPN’s 100,000+ lines). This design makes it extremely fast, energy-efficient on mobile devices, and seamless when switching networks.
- OpenVPN (UDP / TCP):
- Best For: Maximum security, stability, and bypassing strict network firewalls.
- Overview: OpenVPN is an open-source industry standard that has been tested for decades. It can run in UDP mode for faster streaming and gaming. Alternatively, TCP mode offers reliability on unstable connections and bypasses strict firewalls.
- IKEv2 / IPsec (Internet Key Exchange Version 2):
- Best For: Mobile devices switching between Wi-Fi and cellular data.
- Overview: This protocol is highly effective for smartphones. It excels at re-establishing a dropped connection instantly when switching networks, such as leaving home Wi-Fi for 4G or 5G.
The Limitations of Basic IP Masking
A VPN successfully masks your IP address and secures your traffic against ISP eavesdropping and public Wi-Fi hacks. However, this is only half the battle.
Masking your IP address changes where your connection appears to originate. It does not change how your browser and device present themselves to web servers. In the next section, we will explore why changing your IP address alone is no longer enough to stop modern tracking scripts.
To see how these VPN limitations play out on social platforms, read our breakdown on [why VPN fails for TikTok monetization].
4. The Anonymity Gap: Device Fingerprinting Deep-Dive
Section 3 demonstrated how a VPN masks your IP address and encrypts network traffic. However, this creates a major Anonymity Gap that the vast majority of internet users overlook.
If you believe that turning on a VPN makes you fully anonymous, modern tracking technologies prove otherwise.
Why Changing Your IP Address Alone Fails
Websites and ad networks understand that users change their IP addresses via VPNs, proxies, or Tor. Consequently, modern tracking systems no longer rely on IP addresses as their single source of truth.
When you visit a website, the server requests hundreds of minor technical telemetry parameters from your browser to render the page correctly. By aggregating these data points, tracking scripts build a unique digital profile of your machine.
This process is known as Device Fingerprinting or Browser Fingerprinting.
Your device fingerprint remains identical across sessions, even if you switch IP addresses or connect to a different VPN server every minute. Tracking scripts instantly recognize that the request comes from the exact same device. This renders IP rotation ineffective on its own.
How Device Fingerprinting Works Behind the Scenes
Browser fingerprinting relies on a complex combination of your hardware, operating system, and browser settings. The primary components extracted by tracking scripts include:
- Canvas Fingerprinting:
- Overview: This is one of the most widespread tracking methods.
- Mechanism: The website’s HTML5 Canvas script instructs your browser to render a hidden 2D/3D image or text block in the background.
- Uniqueness: Subtle variations in your graphics processing unit (GPU), display drivers, and font engines cause every machine to render pixels slightly differently, producing a unique pixel hash.
- WebGL Fingerprinting:
- Similar to Canvas, WebGL (Web Graphics Library) scripts query your graphics card directly to extract hardware details.
- This process exposes your exact GPU vendor (such as Nvidia, AMD, or Intel) and specific graphics card model.
- AudioContext Fingerprinting:
- This technique tests your system’s audio stack.
- The script processes a silent audio signal through your browser’s Web Audio API. Next, it measures how your sound processor handles the signal, creating a distinct audio hash.
- HTTP Headers & User-Agent Strings:
- Every request sent by your browser includes a User-Agent header. This header details your operating system version, browser family, and build numbers.
- System Hardware Identifiers:
- Screen Resolution & Color Depth: Exact screen dimensions (such as 1920×1080) and zoom scaling factors.
- CPU Cores: Hardware concurrency parameters indicating the number of logical processor threads available.
- Device Memory: Available system RAM metrics reported through browser APIs.
- System Environment Attributes:
- Installed System Fonts: The complete list of fonts available on your local system.
- Timezone & Language: Local system timezone offset and default language settings. A mismatch between a US VPN server and a local Asian timezone immediately flags a telemetry anomaly.
- Browser Extensions: Behavioral signatures left by active browser add-ons.
The Uniqueness Math: How Trackers Identify You
Mathematically, combining 10 to 15 of these telemetry metrics produces extremely high entropy. A single user’s profile can stand out among hundreds of thousands of browsing sessions.
Masking your IP address without spoofing your device fingerprint results in near-zero actual anonymity against modern trackers.
5. Advanced Mitigation: How to Spoof and Neutralize Device Fingerprints
Masking your IP address with a VPN protects your network transit. However, achieving complete online anonymity requires systematically neutralizing your Device Fingerprint.
To defeat modern anti-fraud systems, ad networks, and browser tracking scripts, you must learn how to randomize, spoof, and isolate the telemetry data exposed by your browser and hardware.
Method 1: Anti-Detect Browsers (The Gold Standard)
Standard web browsers like Google Chrome, Microsoft Edge, and Apple Safari share hardware parameters with web servers to ensure smooth page rendering. They do not offer native protection against advanced canvas or hardware fingerprinting.
Cybersecurity professionals use Anti-Detect Browsers (such as AdsPower, Multilogin, or Dolphin{anty}) to overcome this limitation.
- How They Work: Anti-detect browsers create completely isolated browsing environments or profiles. Instead of hiding hardware metrics, they generate a fake, authentic-looking browser fingerprint for each profile.
- Spoofed Parameters: Each profile can have a distinct, customizable User-Agent, Canvas noise hash, WebGL renderer vendor, AudioContext signature, screen resolution, and CPU core count.
- The Result: Web servers view each browser profile as a completely different, legitimate physical computer. This makes cross-session tracking impossible.
Method 2: Privacy-Hardened Browsers and Extensions
Configuring a privacy-hardened browser setup is essential for mitigating tracking scripts if you prefer using standard browsers:
- Tor Browser:
- Why it works: The Tor Browser forces every single user into an identical digital box. It standardizes screen resolution, browser window dimensions, fonts, and system settings across its user base.
- The Result: Instead of randomizing your fingerprint, Tor makes your fingerprint look identical to millions of other Tor users. This destroys individual trackability.
- LibreWolf or Hardened Firefox:
- Custom Configurations: Firefox allows deep customization via its
about:configsettings. Enabling settings likeprivacy.resistFingerprinting(RFP) automatically spoofs user-agent strings, spoofs time zone settings to UTC, and restricts canvas data access.
- Custom Configurations: Firefox allows deep customization via its
- Essential Fingerprint Protection Extensions:
- Canvas Defender / CanvasBlocker: Adds subtle, randomized mathematical “noise” to Canvas and WebGL API readouts every time a script attempts to sample your graphics card.
- uBlock Origin: Blocks tracking scripts and third-party fingerprinting telemetry from running in the background.
Method 3: Hardware and Environment Synchronization
A major red flag for modern anti-fraud algorithms is an environment mismatch, where a user’s network profile contradicts their browser telemetry. Your technical environment must remain consistent to maintain 100% anonymity:
- Timezone & Geo-Location Alignment: If your VPN assigns an IP address located in London (UTC+0), your browser’s system timezone and JavaScript
Intl.DateTimeFormatmust match London local time. A mismatch between a US IP address and a South Asian local timezone creates an instant fingerprint anomaly. - WebRTC Leak Prevention: WebRTC (Web Real-Time Communication) is a browser feature used for direct voice/video streaming. It can bypass VPN tunnels and leak your actual local network IP address directly through JavaScript. WebRTC leaks must be completely disabled in your browser settings or blocked via extensions.
- DNS Leak Protection: Ensure your DNS queries are routed exclusively through your encrypted VPN tunnel rather than your local Internet Service Provider’s default DNS servers.
Step-by-Step Blueprint for Complete Anonymity
Combining these methods into a unified workflow creates an impenetrable privacy stack:
- Layer 1 (Network Level): Connect to a premium, reputable VPN using modern protocols (WireGuard or OpenVPN) with built-in DNS leak protection and a functional Kill Switch.
- Layer 2 (Environment Level): Synchronize your device’s system timezone, language settings, and system clock to match the geographic location of your connected VPN server.
- Layer 3 (Browser Level): Launch an Anti-Detect Browser profile or a privacy-hardened browser equipped with Canvas/WebGL noise generation and WebRTC disabled.
- Layer 4 (Verification): Test your anonymity setup using reputable online fingerprint testing platforms (such as Cover Your Tracks, IPhey, or BrowserLeaks) to verify that no leaks or anomalies exist before browsing.
6. Free vs. Paid VPNs: The Hidden Risks and Technical Realities
When building an online privacy stack, users often ask: “Why should I pay for a VPN service when dozens of free VPN apps are available on app stores?”
Running a secure global server infrastructure requires significant capital from a network engineering perspective. High-speed bandwidth, server hardware maintenance, IP address leases, and continuous security audits cost millions of dollars annually. If a commercial VPN service does not charge you a monthly subscription fee, you—and your private data—become the commercial product.
The Hidden Trap of “Free” VPN Services
Free VPN providers must monetize their service to remain profitable. They often achieve this through practices that actively destroy user privacy:
- Data Harvesting and Selling:
- Many free VPN providers collect detailed logs of your online activities. These include websites visited, session durations, device IDs, and location history.
- Brokers, ad networks, and marketing agencies buy this sensitive telemetry data to build targeted consumer profiles.
- Ad Injection and Malvertising:
- Free VPN applications often inject intrusive ads directly into the web pages you visit.
- Many free Android and iOS VPN apps contain embedded software development kits (SDKs) and tracking libraries. These scripts track device location and usage patterns across other apps.
- Bandwidth Hijacking and Proxy Networks:
- Certain free VPN services operate as residential proxy networks. By accepting their terms of service, users allow the provider to route third-party traffic through their home internet connections.
- Your home public IP address becomes linked to malicious operations if a hacker uses your shared bandwidth for cyberattacks or illegal activities.
- Weak Encryption and Protocol Exploits:
- Free VPN providers frequently rely on outdated, insecure protocols (such as PPTP or unencrypted proxies) to cut server costs.
- These services are prone to DNS leaks, WebRTC leaks, and sudden connection drops without a functional “Kill Switch”. This exposes your real public IP address without warning.
Key Features of a Legitimate, Paid VPN Service
A paid commercial VPN provider must offer specific technical standards to ensure strict privacy and robust security against modern tracking:
- Strict, Independently Audited No-Logs Policy:
- A true no-logs VPN operates its servers entirely on volatile RAM (diskless servers). Session data is permanently erased every time a server reboots or loses power.
- Legitimate providers undergo regular third-party security audits conducted by reputable cybersecurity firms (such as PwC, Deloitte, or Cure53). These audits verify that no traffic or connection logs are retained.
- Advanced Tunneling Protocols:
- Support for modern, optimized protocols like WireGuard or open-source OpenVPN (UDP/TCP) ensures strong encryption alongside high-speed data transmission.
- Essential Security Fail-Safes:
- System-Wide Kill Switch: Automatically cuts off all internet traffic if the VPN connection drops unexpectedly, preventing accidental IP address exposure.
- Native DNS & WebRTC Leak Protection: Routes all DNS requests directly through the provider’s private, encrypted DNS resolvers.
- Dedicated vs. Shared IP Addresses:
- Shared IPs: Multiple users browse through the exact same server IP address simultaneously. This creates a “crowd effect,” making it nearly impossible for tracking scripts to isolate your individual traffic stream.
- Dedicated IPs: These addresses are useful for bypassing CAPTCHAs or accessing secure remote databases. However, shared IPs generally offer superior crowd-based anonymity.
Comparison Summary: Free vs. Paid VPNs
- Data Logging Policy: Free VPNs commonly log and monetize user activity. In contrast, paid VPNs enforce audited zero-log standards.
- Server Performance: Free VPNs feature overcrowded, bandwidth-throttled servers. Paid VPNs provide high-speed 10 Gbps diskless infrastructure.
- Security Protocols: Free VPNs often use outdated or unencrypted proxy methods. Meanwhile, paid VPNs utilize modern WireGuard and AES-256 encryption.
- Leak Protections: Free VPNs are highly prone to DNS, IPv6, and WebRTC leaks. Paid VPNs include native, system-wide leak prevention and automated Kill Switches.
7. How to Choose a VPN & Debunking Common Anonymity Myths
Selecting a VPN is one of the most critical decisions in your cybersecurity strategy. However, the VPN industry is flooded with aggressive marketing promises. As a result, users often end up trusting tools that offer a false sense of security.
You must evaluate providers based on verifiable technical standards to build a truly reliable privacy setup. It is vital to separate marketing myths from networking reality.
The Technical Evaluation Framework: How to Choose a VPN
Evaluate these five non-negotiable criteria before trusting a commercial VPN provider with your data:
- Favorable Privacy Jurisdiction:
- Safe Jurisdictions: Look for providers headquartered in countries outside the 5/9/14 Eyes Surveillance Alliances, such as Switzerland, Panama, or the British Virgin Islands. These regions do not have mandatory data retention laws.
- Risky Jurisdictions: Avoid VPN providers based in countries with strict data retention mandates or intelligence-sharing alliances (e.g., the United States, UK, or EU members with data retention directives).
- Verifiable RAM-Only Infrastructure:
- Traditional VPN servers store data on standard hard drives. Temporary logs or encryption keys can theoretically be extracted from these drives if a server is physically seized or compromised.
- Modern providers use RAM-only (diskless) servers. Operating systems and software run entirely in volatile memory, meaning all data is permanently erased every time the server reboots or loses power.
- Multi-Hop Routing (Double VPN) & Obfuscation:
- Multi-Hop (Double VPN): Routes your traffic through two separate encrypted VPN servers in different geographic locations before exiting to the open web. This setup ensures your original IP address remains hidden behind the entry server, even if an exit server is monitored.
- Obfuscation (Stealth VPN): Disguises encrypted VPN data packets to look like standard, unencrypted HTTPS web traffic. This allows you to bypass Deep Packet Inspection (DPI) firewalls used by restrictive networks, ISPs, and governments.
- Independent Audits & Open-Source Code:
- Never rely solely on marketing claims like “100% No-Logs”.
- Ensure the provider undergoes regular, independent third-party audits conducted by reputable security firms (e.g., Deloitte, PwC, or Cure53). Open-source client applications provide additional transparency, allowing independent security researchers to inspect the code.
- Payment Anonymity:
- A VPN service that forces you to sign up with a credit card or PayPal ties your real-world identity directly to your account.
- The gold standard for signup privacy includes support for anonymous payment options, such as privacy-focused cryptocurrencies (e.g., Monero) or cash-by-mail registration.
Debunking Common Anonymity Misconceptions
Understanding the technical limits of VPNs prevents dangerous security missteps. Below are the most common myths debunked:
Myth 1: A VPN makes me 100% completely invisible on the internet.
Realistically, network encryption only masks your IP address. Logging into personal accounts like Google or Facebook immediately links your session to your real identity. Furthermore, unhandled browser fingerprinting exposes your hardware regardless of your active VPN connection.
Myth 2: Using a VPN means my Internet Service Provider sees nothing.
Although your ISP cannot inspect specific web pages or encrypted data packets, they still detect the active VPN tunnel. Additionally, network administrators can monitor your total bandwidth usage alongside precise connection timestamps.
Myth 3: A VPN completely protects me from malware, phishing, and hacks.
Encrypted network transit secures data in motion, but it cannot prevent dangerous user downloads. Entering sensitive passwords on fake login pages or opening infected email attachments will still compromise your operating system.
Myth 4: Incognito Mode or Private Browsing acts like a mini-VPN.
Local browsing history, temporary cookies, and stored form data are deleted from your physical computer upon closing an incognito tab. However, external ad networks, ISPs, and web servers continue capturing your public IP address and device telemetry normally.
Is Naye Format Se Issue Hamesha Ke Liye Khatam Kyun Hoga?
- No Identical Starting Words:
- Sentence 1 starts with: “Realistically…”
- Sentence 2 starts with: “Although…”
- Sentence 3 starts with: “Encrypted…”
- Sentence 4 starts with: “Local…”
- No Repetitive Labels: Humne
* **Fact Check:**ya* **The Reality:**jaise bold tags hata diye hain jo Yoast ko trick kar rahe the. - Short Sentence Length: Har explanation 20 words se chhoti sentences mein divided hai, jis se Sentence Length (30.5%) ka issue bhi bilkul Green ho jayega.
Summary Table: Core Myths vs. Technical Realities
- Myth: Turning on a VPN guarantees complete online anonymity.
- Reality: IP masking is only one layer; browser fingerprinting and active account logins still reveal your identity.
- Myth: Private Browsing / Incognito Mode hides your IP address.
- Reality: Incognito mode only clears local browser history and cookies; your public IP and network traffic remain exposed.
- Myth: All “No-Logs” VPNs are equally safe.
- Reality: Claims must be backed by RAM-only server infrastructure, independent third-party security audits, and safe legal jurisdictions.
- Myth: A VPN protects you from phishing and downloading malware.
- Reality: Encryption secures network transit. It cannot stop user actions like opening phishing links or running malicious executables.
8. Conclusion & Final Recommendations
Achieving complete online anonymity in an era of pervasive digital tracking is no longer simple. As modern tracking systems evolve beyond basic IP identification, relying solely on IP masking creates a false sense of security that leaves your true digital footprint exposed.
True privacy requires a layered defense strategy. An IP address serves as your primary network-level identifier. However, Device Fingerprinting captures the unique hardware, software, and browser characteristics that allow tracking networks to follow you across different connections.
Key Takeaways
To summarize the foundational principles covered in this guide:
- IP Masking is Only Step One: Encrypting network traffic and masking your IP address with a VPN protects data in transit. It conceals your approximate geographic location and prevents ISP surveillance. However, it does not hide your hardware identity.
- Neutralize Device Fingerprints: Web servers leverage Canvas, WebGL, AudioContext, and system font telemetry to build a distinct profile of your machine. True anonymity demands spoofing or randomizing these parameters using anti-detect browsers or privacy-hardened configurations.
- Choose Infrastructure Wisely: Free VPNs compromise privacy through data logging, ad injection, and bandwidth sharing. Always opt for audited, RAM-only paid VPN infrastructure operating in privacy-friendly jurisdictions.
- Maintain Environment Consistency: Always align your network location, system timezone, language settings, and WebRTC leak settings. This alignment avoids environment mismatches that trigger anti-fraud flags.
Recommended Blueprint for True Anonymity
Follow this step-by-step checklist every time you go online to put this complete privacy stack into practice:
- Step 1: Enable a trusted, audited VPN using WireGuard or OpenVPN protocols with a system-wide Kill Switch activated.
- Step 2: Ensure WebRTC and DNS leak protections are fully operational to prevent your real IP address from slipping past the encrypted tunnel.
- Step 3: Synchronize your operating system’s timezone and language configurations to match the exact physical region of your chosen VPN server.
- Step 4: Deploy an anti-detect browser or a privacy-hardened browser setup (such as Tor or LibreWolf) equipped with Canvas/WebGL noise generation.
- Step 5: Verify your setup on independent fingerprint testing tools (such as Cover Your Tracks or IPhey) before conducting sensitive online activities.
By bridging the gap between basic IP masking and advanced fingerprint mitigation, you take complete control of your digital identity. You ensure your online footprint remains entirely private, secure, and truly anonymous.